
What to know: The White House confirmed Cairncross’s departure; CBS reported that he was fired, citing multiple sources. Reports say Davies will serve in an acting capacity. The timing alone does not establish why he left or what caused the separate outages.
White House Replaces Cyber Director Amid Major Outages. What Does It Mean for Security?
Sean Cairncross is leaving as national cyber director, and Pentagon technology chief Kirsten Davies is expected to take over in an acting capacity. The move follows a week of major outages, but a common cyberattack has not been established.
Jump to a section
A week of disruptions left people unable to rely on services they usually take for granted. Now the White House official responsible for coordinating federal cyber policy is leaving, just as the public is asking what went wrong.
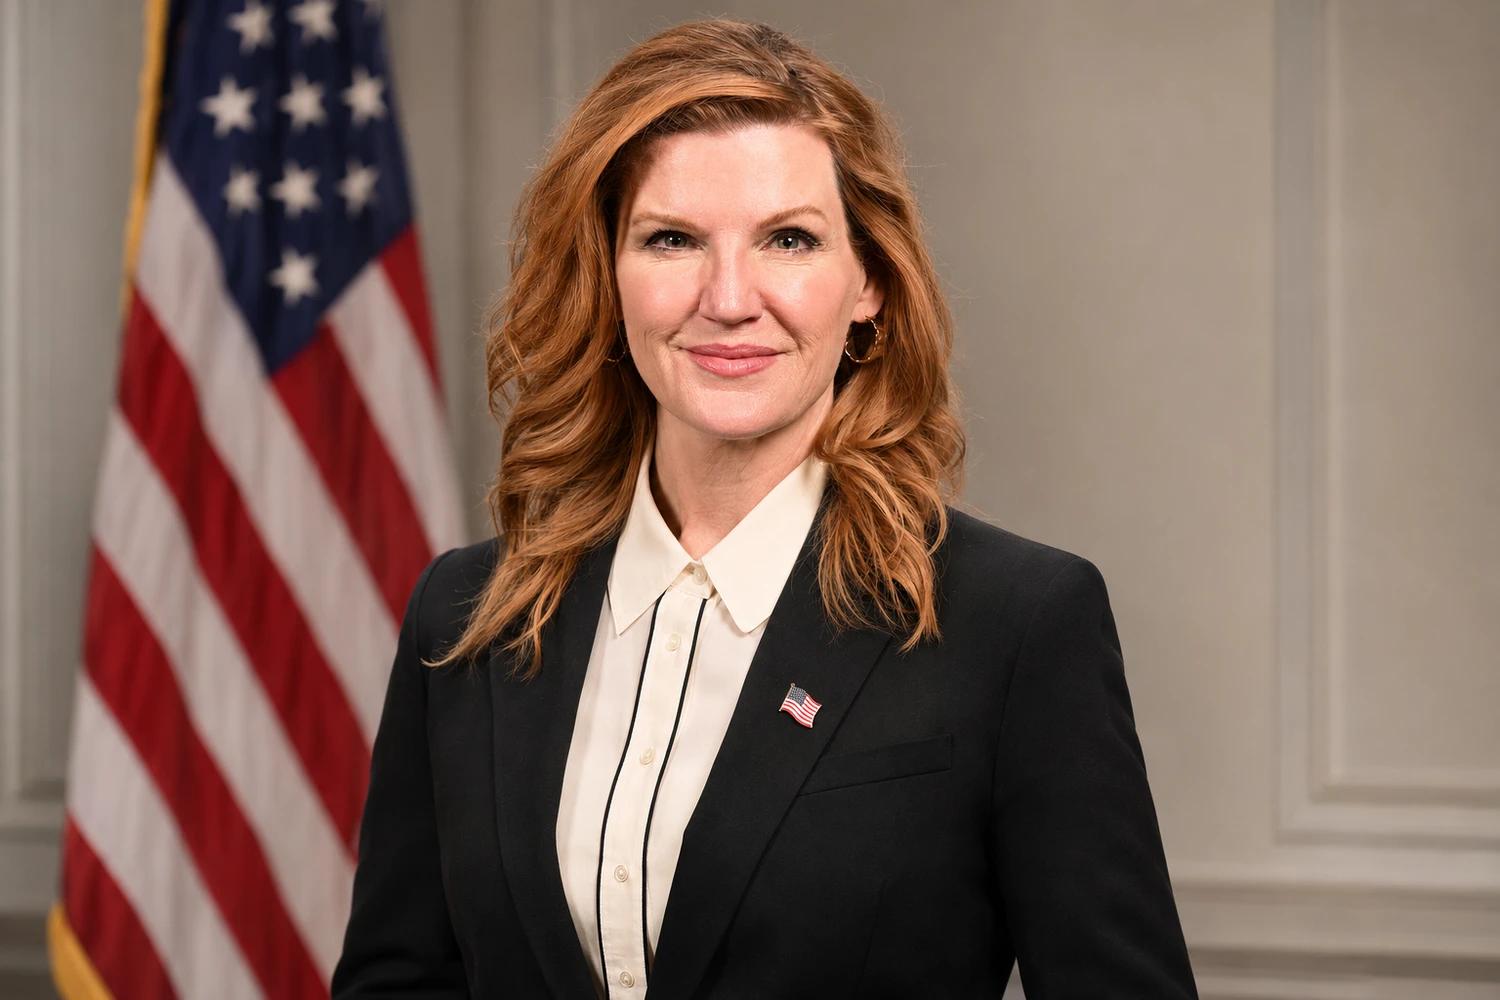
A White House official confirmed that National Cyber Director Sean Cairncross was leaving, CBS reported on November 19. Multiple sources told CBS that Cairncross was fired. CNN reported that Kirsten Davies, the Pentagon’s chief information officer, would take over in an acting capacity.
The move follows disruptions affecting banking, Microsoft services, air travel and a National Security Agency network. The public timing is clear. Whether the outages drove the personnel decision, and how individual incidents were assessed inside the administration, is not established by the public evidence reviewed here.
What the national cyber director actually does
The national cyber director advises the president and coordinates cybersecurity policy and strategy across the federal government. The job is different from running the Cybersecurity and Infrastructure Security Agency, or CISA, and it does not make its holder the operator of private banks, airlines or cloud services.
That division matters. A leadership change can affect coordination, priorities and communication. It does not establish that the departing official caused an outage or that the replacement can directly repair a company’s software. CBS describes the office’s coordinating role; CISA describes its own mission as the national coordinator for critical infrastructure security and resilience.
Davies became the Pentagon’s chief information officer in December 2025 and oversees its technology and cybersecurity strategy, according to her official Defense Department biography. She previously held senior security and technology roles in the private sector, including at Unilever, Axios reports. Contemporary reports describe her new appointment as acting, rather than a completed permanent confirmation.
Were the outages connected?
Authorities investigating the disruptions had seen nothing indicating they were related, Homeland Security Secretary Markwayne Mullin told lawmakers, according to CBS. That is an assessment based on the information available to officials, not a public forensic proof of every cause.
The NSA said its network experienced temporary degradation during scheduled routine maintenance, while mission-critical capabilities remained operational. Our NSA Net report separates that statement from details officials have not publicly explained.
Chase described its earlier banking disruption as a technical issue. It later reported a separate incident involving outside providers and customer marketing information. Our report on those provider disclosures explains why the two should not be merged into one event.
Microsoft’s disruption had its own reported timeline. Our Microsoft 365 outage analysis looks at the effects and the limits of what could be established about the cause and costs. Similar consequences do not prove a shared trigger.
Where AI fits, and where it does not
The FBI’s ARTEX warning describes a real threat: attackers have used AI-assisted tools in intrusions. Separately, the European Commission has confirmed an AI-assisted cyberattack, as we explain in our report on that incident.
Those facts do not establish that ARTEX or another AI tool caused the U.S. outages, or that the Commission incident and the U.S. disruptions were part of one campaign. A genuine threat can exist at the same time as unrelated technical failures.
The harder policy question is how to improve resilience against both. Organizations need to close genuine security gaps without turning every update into an avoidable operational crisis. That requires tested changes, clear ownership, backups that work and a way to communicate when normal channels fail.
What people and businesses can do
- Check the specific service. Use the provider’s official status page or a known app. Do not assume a disruption elsewhere proves your account was hacked.
- Be cautious with urgent “restoration” messages. Attackers can exploit confusion. Do not share a password or login code, and verify instructions through a known channel.
- Keep a fallback for essential tasks. Businesses should identify critical services, their owners and dependencies, then test how staff will communicate and authorize work during an outage.
- Respond to actual exposure. If you entered credentials into a suspicious page or see unauthorized activity, contact the provider through a trusted route and follow the relevant recovery process.
Our guide to protecting a business from hackers offers steps for access controls and incident planning. Our outage phishing coverage explains how to handle fake service-restoration messages.
Davies inherits a public looking for answers and a system in which responsibility is spread across government agencies and private operators. The test will be whether they can communicate what they know, investigate what they do not and keep essential services working through both attacks and ordinary failures.